


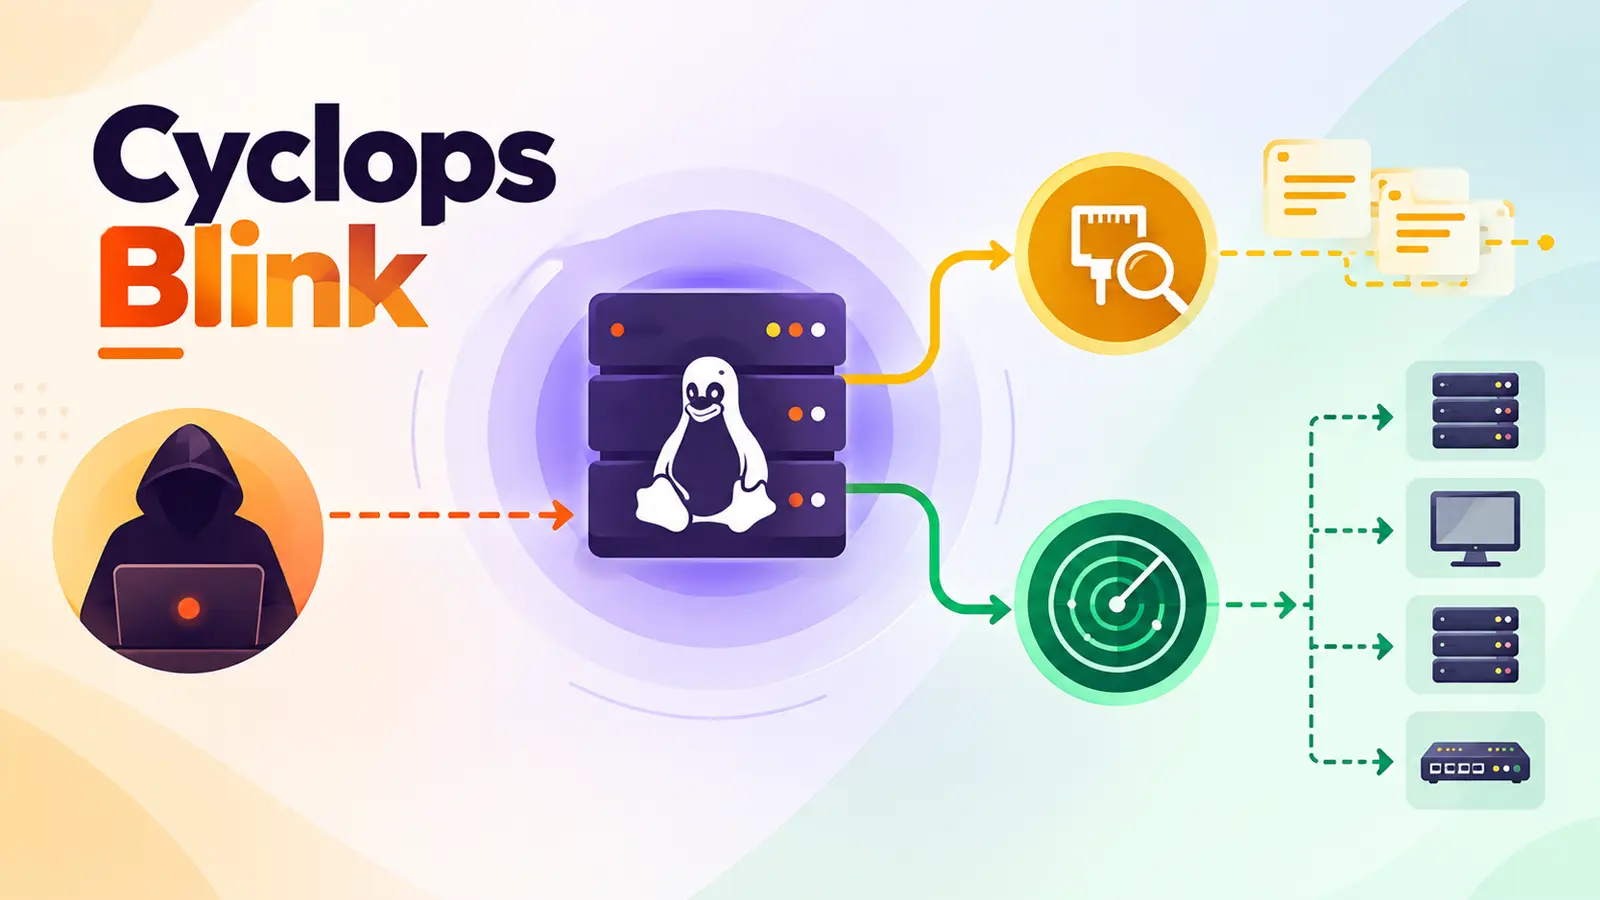
Cyclops Blink has returned, offering attackers a more comprehensive view of corporate networks This article explores ports used cyclops. . An attacker could use one compromised device as a reconnaissance point, a staging area for follow-up payloads, and a secure foothold with visibility into privileged management networks and multiple internal address ranges.
The command-and-control channel employs outbound TLS connections and a custom protocol, bypassing regular web traffic. Scanning Converts Devices Into Sensors The internal scanner identifies local IPv4 networks and tests either selected ports by operators or a list linked to administration, file sharing, messaging, directory services, web applications, network monitoring, VPNs, and virtualization.
Indicators of compromise (IoCs): - C2 IP address 89.34.96.56: Hard-coded Cyclops Blink command-and-control server - C2 TCP ports 43856, 49172: Outbound ports used for Cyclops Blink command-and-control communications - File path /lib/tz/timezonecheck: Persistent installation location used by analyzed 2026 samples - File name timezonecheck: Name used by the malicious Linux executable and persistence component - Init service /etc/init.d/timezonecheck: SysV init script created to launch the implant - Startup links /etc/rc2.d/S89timezonecheck, /etc/rc3.d/S89timezonecheck, /etc/rc4.d/S89timezonecheck, /etc/rc5.d/S89timezonecheck: SysV runlevel startup links used for persistence - Process name kworker01: Controller process name intended to resemble a normal Linux worker process - User-Agent: Distinctive HTTP and DNS-over-HTTPS request header used by the malware - Note: IP addresses and domains are intentionally defanged to prevent accidental resolution or hyperlinking.


