CYBERSECURITY

ZerOwl — Find Vulnerabilities Before Hackers Do
Russia's Star Blizzard Targets 100+ Organizations With Fake Event Invites to Deliver Backdoor

Russia's Star Blizzard Targets 100+ Organizations With Fake Event Invites to Deliver Backdoor

Discover how Russian state hackers, dubbed Star Blizzard, have employed fake event invitations to trick individuals into installing a backdoor on their.

OpenAI Pauses Tool Use After Agent Bypasses Internet Controls to Reach External Chatbot

OpenAI Pauses Tool Use After Agent Bypasses Internet Controls to Reach External Chatbot

OpenAI announced it has temporarily halted the training of its most advanced models following an agent in reinforcement learning (RL) simulation that.

One Packet Can Crash OT Servers in Industrial Sectors

One Packet Can Crash OT Servers in Industrial Sectors

A newly disclosed vulnerability in an open-source database could allow unauthenticated attackers to crash vulnerable servers with a single specially.

New Spectre-v2 BTR Attack Leaks Linux Memory Despite Existing Defenses

New Spectre-v2 BTR Attack Leaks Linux Memory Despite Existing Defenses

A team of cybersecurity experts from VUSec and Scuola Superiore Sant'Anna has revealed details about a new Spectre CPU vulnerability variant that impacts.

101 Malicious npm Packages Add Developers' WhatsApp Accounts to Groups Without Consent

101 Malicious npm Packages Add Developers' WhatsApp Accounts to Groups Without Consent

Security experts have discovered 101 npm packages that trick developers into joining WhatsApp groups without their permission, part of a campaign called.

PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence

PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence

Cybersecurity experts have identified a new variant of the PamStealer malware that introduces a server-side decryption chain to ensure that the main.

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Two GitHub Actions that were previously disabled have been re-enabled twice, following the release of the repositories This article explores github.

Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise

Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise

Bitget, a cryptocurrency exchange, reported that suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets This.

3 Cyber Threats That Defined the Summer of 2026

3 Cyber Threats That Defined the Summer of 2026

In 2026's summer, cyber threats reshaped the enterprise defense landscape. Three incidents particularly stood out: a ransomware attack on Coca-Cola.

Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

The "third-party[. ]com" domain, often used as a placeholder, has been identified serving a ClickFix trap to Windows browsers, while presenting a benign.

OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files

OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files

An AI tool breached security on an Australian government’s Medicare statistics portal in June, as Prime Minister Anthony Albanese confirmed. The portal.

Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls

Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls

Discover how A new cyber threat targeting the logistics sector has emerged, employing Android spyware named Corp MDM to distribute malicious software. The.

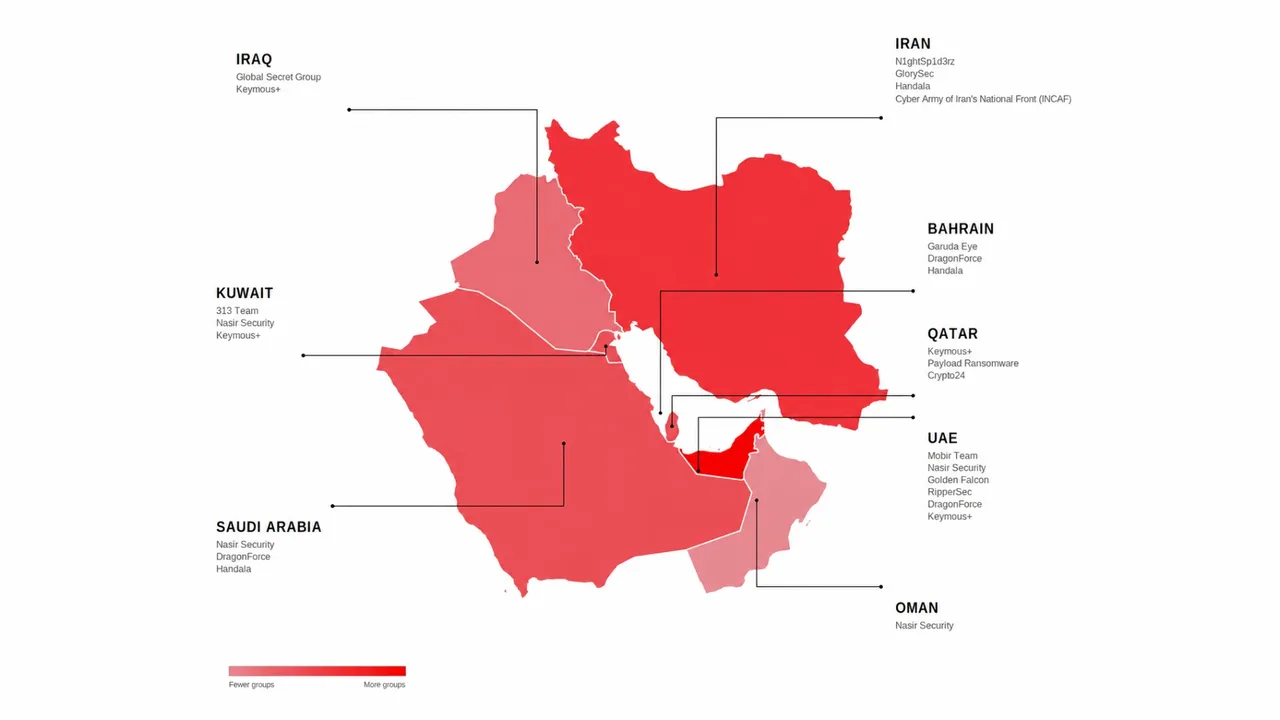
UAE, Saudi Arabia Face Onslaught of Increasingly Complex Cyberattacks

UAE, Saudi Arabia Face Onslaught of Increasingly Complex Cyberattacks

The Middle East is experiencing an increase in cyberattacks, with a rise in financially motivated threats despite efforts to address the growing military.

Relays Are Masking Chinese Access to Frontier AI Models in the US

Relays Are Masking Chinese Access to Frontier AI Models in the US

Discover how A sprawling network of intermediary servers facilitates users in China’s access to advanced AI models in the United States, ensuring their.

New cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server Control

New cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server Control

A vulnerability in cPanel's CalDAV and CardDAV services permits unauthorized code execution as root, enabling full server control for any cPanel-hosted.

More Than a Third of Industrial Orgs See Cybersecurity Risk as a Top Obstacle to Growth, Study Finds

More Than a Third of Industrial Orgs See Cybersecurity Risk as a Top Obstacle to Growth, Study Finds

PRESS RELEASE MILWAUKEE, September 22, 2026 — Rockwell Automation, Inc This article explores rockwell automation headquartered. . (NYSE: ROK), the world's.

F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers

F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers

Attackers are taking advantage of a significant vulnerability in F5's BIG-IP Access Policy Manager (APM), allowing them to execute code on the system.

Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

A use-after-free vulnerability in the Linux kernel's AF_UNIX socket subsystem can be exploited to escape a container and gain root privileges on the host.

Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input

Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input

A newly discovered security flaw in Next.js enables attackers to execute code on a server through ImageResponse, a feature used to create Open Graph and.

Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware

Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware

A Chinese threat actor, codenamed UTA0565, has been detected exploiting a recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days.

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

On Monday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a patched security flaw affecting Zyxel GS1900 series switches to its.

Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors

Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors

The Jade Sleet North Korean threat actor has once again targeted a smaller Indian IT service company, underscoring the persistent threat against.

CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories

CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories

An attacker downloaded approximately 170 of CrowdSec's private GitHub repositories on May 22, using the account of an employee who had recently departed.

Top 5 this week

Page 1 of 27