CYBERSECURITY

ZerOwl — Find Vulnerabilities Before Hackers Do
APT36 and SideCopy Launch Cross-Platform RAT Campaigns Against Indian Entities

APT36 and SideCopy Launch Cross-Platform RAT Campaigns Against Indian Entities

Numerous campaigns aimed at infiltrating Windows and Linux environments with remote access trojans that can steal confidential information and guarantee.
Do We Know Enough About the Data That Underlies AIs Rise?

Do We Know Enough About the Data That Underlies AIs Rise?

ANALYSIS It is undeniable that using AI can unlock (considerable) business benefits This article explores ai taken businesses. . By automating simple or.

Exposed Training Open the Door for Crypto-Mining in Fortune 500 Cloud Environments

Exposed Training Open the Door for Crypto-Mining in Fortune 500 Cloud Environments

For internal testing, security education, and product demonstrations, intentionally vulnerable training applications are frequently utilized. Because they.

SSHStalker Botnet Uses IRC C2 to Control Linux Systems via Legacy Kernel Exploits

SSHStalker Botnet Uses IRC C2 to Control Linux Systems via Legacy Kernel Exploits

Details of a new botnet operation known as SSHStalker, which uses the Internet Relay Chat (IRC) communication protocol for command-and-control (C2).

Microsoft Patches 59 Vulnerabilities Including Six Actively Exploited Zero-Days

Microsoft Patches 59 Vulnerabilities Including Six Actively Exploited Zero-Days

Microsoft fixed 59 bugs in its software on Tuesday, including six that it claimed had been exploited in the wild This article explores security flaws.

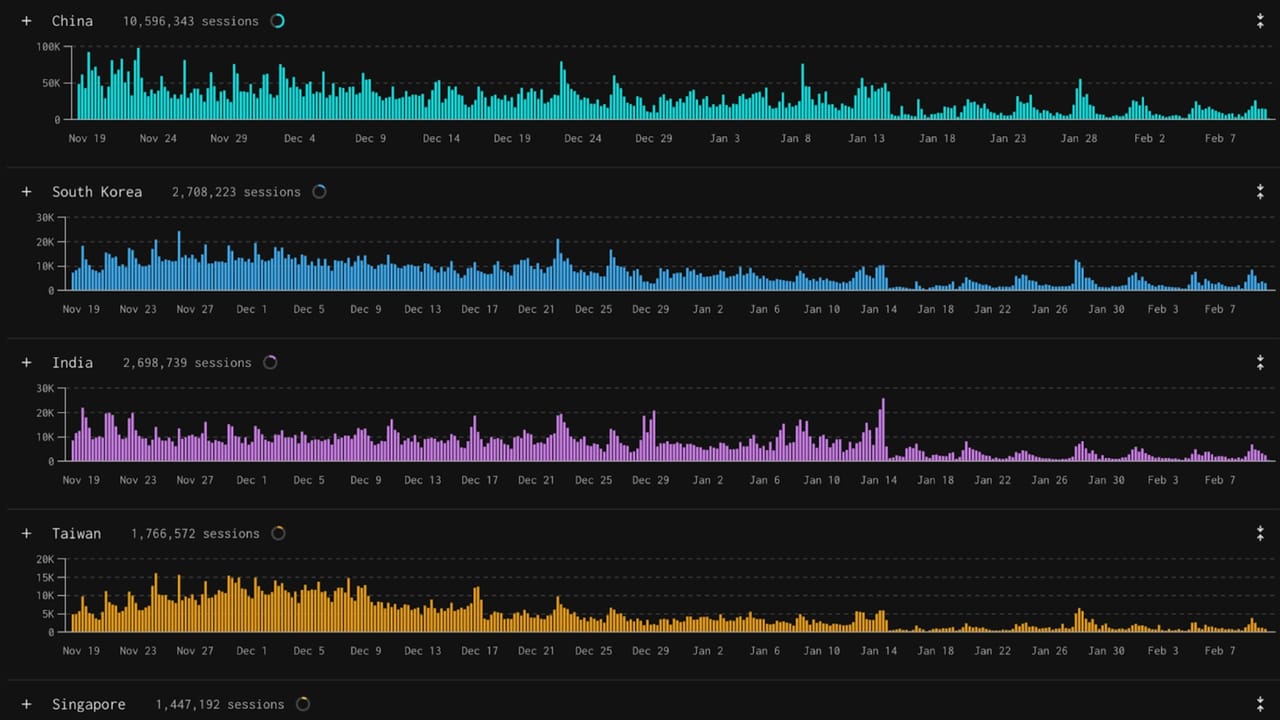
Asia Struggles to Reduce Back Telnet Traffic in the Area

Asia Struggles to Reduce Back Telnet Traffic in the Area

Despite a recent critical vulnerability and the general insecurity of the protocol, many devices and consumer-grade routers in the Asia-Pacific region.

ZeroDayRAT Is Textbook Stalkerware in Bypassing MFA

ZeroDayRAT Is Textbook Stalkerware in Bypassing MFA

A new family of malware bundles information-stealing, surveillance, and spyware features for mass-market criminals This article explores zerodayrat family.

Reynolds Ransomware Embeds BYOVD Driver to Disable EDR Security Tools

Reynolds Ransomware Embeds BYOVD Driver to Disable EDR Security Tools

Researchers studying cybersecurity have revealed information about the Reynolds family of emerging ransomware, which has an integrated bring your own.

OT Attacks Get Scary With 'Living-off-the-Plant' Techniques

OT Attacks Get Scary With 'Living-off-the-Plant' Techniques

Due to attackers' lack of knowledge about custom and legacy systems, operational technology (OT) cyberattacks have been comparatively mild in recent years.

What Organizations Need to Change When Managing Printers

What Organizations Need to Change When Managing Printers

Question: There is currently no protection for managed printers This article explores protection managed printers. . What leadership-level adjustments are.

TransUnion's Real Networks Deal Focuses on Robocall Blocking

TransUnion's Real Networks Deal Focuses on Robocall Blocking

NEWS BRIEF TransUnion is concentrating on improving voice and SMS fraud protection services for businesses, as evidenced by its announcement last week.

From Ransomware to Residency: Inside the Rise of the Digital Parasite

From Ransomware to Residency: Inside the Rise of the Digital Parasite

Are ransomware and encryption still the defining signals of modern cyberattacks, or has the industry been too fixated on noise while missing a more.

ZAST.AI Raises $6M Pre-A to Scale "Zero False Positive" AI-Powered Code Security

ZAST.AI Raises $6M Pre-A to Scale "Zero False Positive" AI-Powered Code Security

ZAST, Seattle, USA, January 5, 2026.AI reported that a $6 million Pre-A funding round was completed This article explores vulnerabilities ai garnered.

Warlock Ransomware Breaches SmarterTools Through Unpatched SmarterMail Server

Warlock Ransomware Breaches SmarterTools Through Unpatched SmarterMail Server

Last week, SmarterTools verified that an unpatched SmarterMail instance was used by the Warlock (also known as Storm-2603) ransomware gang to compromise.

A Five-Step Guide to Creating a Reliable Security Orchestration in 2026

A Five-Step Guide to Creating a Reliable Security Orchestration in 2026

Automation has reached a new level This article explores automation consistently. . What started out as ticket bots and ad hoc scripting has evolved into.

Cloud Infrastructure Becomes Crime Bots with TeamPCP

Cloud Infrastructure Becomes Crime Bots with TeamPCP

A threat actor is methodically focusing on exposed and improperly configured cloud management services and control interfaces in order to take over.

BYOVD Black Basta Bundles With Ransomware Payload

BYOVD Black Basta Bundles With Ransomware Payload

With a new weapon in its toolbox, the notorious Black Basta ransomware gang has returned This article explores driver ransomware threat. . The Symantec.

China-Associated UNC3886 Launches Cyber Espionage Campaign Against Singapore Telecom Sector

China-Associated UNC3886 Launches Cyber Espionage Campaign Against Singapore Telecom Sector

Singapore's Cyber Security Agency (CSA) announced Monday that its telecommunications industry was the target of UNC3886, a cyber espionage group with ties.

SolarWinds Web Help Desk Exploited for RCE in Multi-Stage Attacks on Exposed Servers

SolarWinds Web Help Desk Exploited for RCE in Multi-Stage Attacks on Exposed Servers

Microsoft has disclosed that it witnessed a multi-phase intrusion in which the threat actors used internet-exposed SolarWinds Web Help Desk (WHD).

⚡ Weekly Recap: Notepad++ Hack, 31Tbps DDoS, AI Skill Malware, LLM Backdoors, and More

⚡ Weekly Recap: Notepad++ Hack, 31Tbps DDoS, AI Skill Malware, LLM Backdoors, and More

Malware and exploits are no longer the only sources of cyberthreats This article explores malware exploits. . They are becoming present in the ecosystems.

How Top CISOs Solve Burnout and Speed up MTTR without Extra Hiring

How Top CISOs Solve Burnout and Speed up MTTR without Extra Hiring

Discover how Why, despite investing heavily in security tools, do SOC teams continue to burn out and miss SLAs? Stealthy threats continue to get through.

Bloody Wolf Targets Uzbekistan, Russia Using NetSupport RAT in Spear-Phishing Campaign

Bloody Wolf Targets Uzbekistan, Russia Using NetSupport RAT in Spear-Phishing Campaign

A campaign aimed at Russia and Uzbekistan to infect systems with the remote access trojan NetSupport RAT has been connected to the threat actor Bloody.

BeyondTrust Addresses a Serious Pre-Auth RCE Risk in PRA and Remote Support

BeyondTrust Addresses a Serious Pre-Auth RCE Risk in PRA and Remote Support

Updates from BeyondTrust have been made available to fix a serious security vulnerability that affects Privileged Remote Access (PRA) and Remote Support.

Voice: The Biggest Security Gap You’re Ignoring

Voice: The Biggest Security Gap You’re Ignoring

According to Crowdstrike, voice-based attacks increased 442% in 2024 This article explores voice security tier. . By 2027, DeepStrike predicts that losses.

Exposure Management Is at a Breaking Point That’s Forcing a Reset

Exposure Management Is at a Breaking Point That’s Forcing a Reset

Security teams have plenty of data, tools, and alerts, but exposure management is at a breaking point that is forcing a reset This article explores ctem.

The New Security Risk Is Cloud Complexity

The New Security Risk Is Cloud Complexity

Discover how Complex IT and cloud environments are not purposefully created by enterprise security teams. Growth frequently results in complexity.

Top 5 this week

Page 18 of 26