CYBERSECURITY

ZerOwl — Find Vulnerabilities Before Hackers Do
Winter Olympics Could Share Podium With Cyberattackers

Winter Olympics Could Share Podium With Cyberattackers

Cybercriminals will also be vying for gold when the Milano Cortina Winter Games start on February 6. Experts caution that everything is possible, from ransomware and distributed denial-of-
Vulnerabilities Surge, But Messy Reporting Blurs Picture

Vulnerabilities Surge, But Messy Reporting Blurs Picture

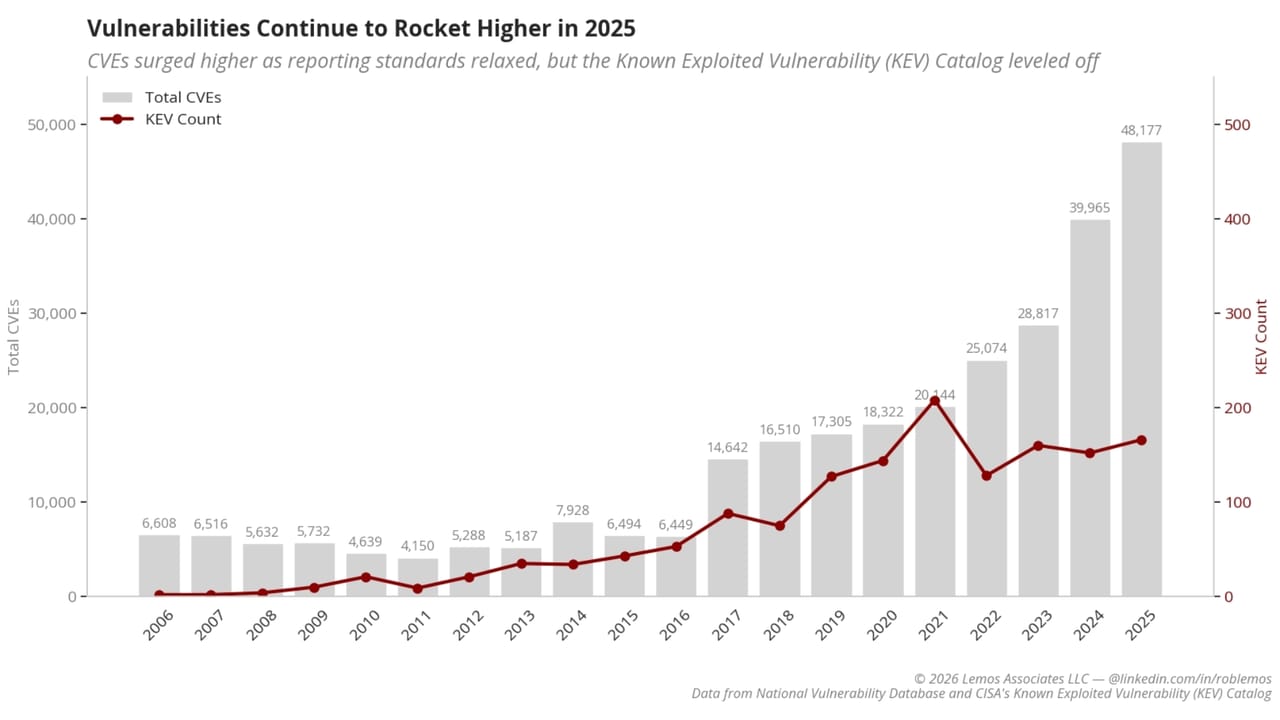
Vulnerability reports set yet another record this year This article explores cve identified vulnerabilities. . According to data analyzed from the National Vulnerability Database (NVD), 48

Predator Spyware Sample Indicates 'Vendor-Controlled' C2

Predator Spyware Sample Indicates 'Vendor-Controlled' C2

For a long time, commercial spyware vendors have defended their companies by arguing that they sell their products to government agencies in support of national security and law enforcemen

LOTUSLITE Backdoor Targets U.S. Policy Entities Using Venezuela-Themed Spear Phishing

LOTUSLITE Backdoor Targets U.S. Policy Entities Using Venezuela-Themed Spear Phishing

Security experts have revealed information about a new campaign that uses politically themed lures to deliver a backdoor known as LOTUSLITE to U.S. government and policy entities. The targ

Cisco Patches Zero-Day RCE Exploited by China-Linked APT in Secure Email Gateways

Cisco Patches Zero-Day RCE Exploited by China-Linked APT in Secure Email Gateways

Almost a month after the company revealed that a China-nexus advanced persistent threat (APT) actor codenamed UAT-9686 had exploited a maximum-severity security flaw affecting Cisco AsyncO

APT Associated with China Uses Sitecore Zero-Day to Attack American Critical Infrastructure

APT Associated with China Uses Sitecore Zero-Day to Attack American Critical Infrastructure

Since at least last year, critical infrastructure sectors in North America have been the target of a threat actor that is probably affiliated with China This article explores ttps uat 8837

ThreatsDay Bulletin: AI Voice Cloning Exploit, Wi-Fi Kill Switch, PLC Vulns, and 14 More Stories

ThreatsDay Bulletin: AI Voice Cloning Exploit, Wi-Fi Kill Switch, PLC Vulns, and 14 More Stories

There is never a quiet moment on the internet This article explores apple intelligence uphold. . There are new security issues, scams, and hacks every week.

The stories this week de

Model Security Is the Wrong Frame – The Real Risk Is Workflow Security

Model Security Is the Wrong Frame – The Real Risk Is Workflow Security

Security teams continue to concentrate on safeguarding the models themselves even as AI copilots and assistants are integrated into daily tasks This article explores safeguarding models ai

Four Antiquated Practices That Will Destroy Your SOCs MTTR in 2026

Four Antiquated Practices That Will Destroy Your SOCs MTTR in 2026

Even in 2026, a lot of SOCs are still using procedures and tools that were created for a completely different threat environment This article explores security tools soc. . Outdated proced

Trio of Critical Bugs Spotted in Delta Industrial PLCs

Trio of Critical Bugs Spotted in Delta Industrial PLCs

One high-severity vulnerability and three critical-severity vulnerabilities have been found in a brand of programmable logic controller (PLC) that is widely used in Asian industrial settin

Microsoft Legal Action Disrupts RedVDS Cybercrime Infrastructure Used for Online Fraud

Microsoft Legal Action Disrupts RedVDS Cybercrime Infrastructure Used for Online Fraud

Microsoft declared on Wednesday that it has launched a "coordinated legal action" in the United States and the United Kingdom to stop RedVDS, a cybercrime subscription service that has all

'VoidLink' Malware Poses Advanced Threat to Linux Systems

'VoidLink' Malware Poses Advanced Threat to Linux Systems

A sophisticated, cloud-first malware framework created by actors connected to China that aims to create persistent access to cloud and container environments may soon pose a new threat to

Taiwan Endures Greater Cyber Pressure From China

Taiwan Endures Greater Cyber Pressure From China

China's cyber-threat groups are still intensifying their attacks on Taiwan, increasing cyber activity against the vital infrastructure of the self-governing island and appearing to carry o

ServiceNow Patches Critical AI Platform Flaw Allowing Unauthenticated User Impersonation

ServiceNow Patches Critical AI Platform Flaw Allowing Unauthenticated User Impersonation

ServiceNow has revealed information about a critical security vulnerability affecting its ServiceNow AI Platform that has been fixed This article explores vulnerability affecting serviceno

Retail, Services Industries Under Fire in Oceania

Retail, Services Industries Under Fire in Oceania

According to recent data, hackers are increasingly focusing on businesses in non-critical industries like retail and construction in Australia and New Zealand This article explores repercu

Microsoft Disrupts Cybercrime Service RedVDS

Microsoft Disrupts Cybercrime Service RedVDS

Microsoft recently took part in a concerted legal effort to stop RedVDS, a cybercrime service that defrauded victims of millions of dollars This article explores stop redvds cybercrime. .

New Malware Campaign Delivers Remcos RAT Through Multi-Stage Windows Attack

New Malware Campaign Delivers Remcos RAT Through Multi-Stage Windows Attack

Cybersecurity researchers have revealed information about a new campaign called SHADOW#REACTOR, which uses an evasive multi-stage attack chain to establish persistent, covert remote access

CISA Warns of Active Exploitation of Gogs Vulnerability Enabling Code Execution

CISA Warns of Active Exploitation of Gogs Vulnerability Enabling Code Execution

A high-severity security vulnerability affecting Gogs has been actively exploited, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA), which has added it to its

n8n Supply Chain Attack Abuses Community Nodes to Steal OAuth Tokens

n8n Supply Chain Attack Abuses Community Nodes to Steal OAuth Tokens

In order to obtain developers' OAuth credentials, threat actors have been seen uploading eight packages to the npm registry under the guise of integrations intended for the n8n workflow au

⚡ Weekly Recap: AI Automation Exploits, Telecom Espionage, Prompt Poaching & More

⚡ Weekly Recap: AI Automation Exploits, Telecom Espionage, Prompt Poaching & More

One thing became evident this week: minor mistakes can quickly get out of control This article explores 2024 vmware vulnerabilities. . Once fundamental precautions were disregarded, time-s

GoBruteforcer Botnet Targets Crypto Project Databases by Exploiting Weak Credentials

GoBruteforcer Botnet Targets Crypto Project Databases by Exploiting Weak Credentials

In order to create a botnet that can brute-force user passwords for services like FTP, MySQL, PostgreSQL, and phpMyAdmin on Linux servers, a recent wave of GoBruteforcer attacks has target

Anthropic Launches Claude AI for Healthcare with Secure Health Record Access

Anthropic Launches Claude AI for Healthcare with Secure Health Record Access

The latest artificial intelligence (AI) company to reveal a new feature set that enables users of its Claude platform to comprehend their health data is Anthropic This article explores wel

Researchers Uncover Service Providers Fueling Industrial-Scale Pig Butchering Fraud

Researchers Uncover Service Providers Fueling Industrial-Scale Pig Butchering Fraud

Two service providers that give online criminal networks the infrastructure and tools they need to support the pig butchering-as-a-service (PBaaS) economy have been identified by cybersecu

New n8n Vulnerability (9.9 CVSS) Lets Authenticated Users Execute System Commands

New n8n Vulnerability (9.9 CVSS) Lets Authenticated Users Execute System Commands

N8n has been found to have a new critical security flaw. An authenticated attacker might be able to run arbitrary system commands on the underlying host. The vulnerability has a CVSS score

Cybercriminals Abuse Google Cloud Email Feature in Multi-Stage Phishing Campaign

Cybercriminals Abuse Google Cloud Email Feature in Multi-Stage Phishing Campaign

During a 14-day period in December 2025, attackers were seen sending 9,394 phishing emails to about 3,200 customers.

The misuse of Application Integration's "Send Email" task, which

The ROI Problem in Attack Surface Management

The ROI Problem in Attack Surface Management

Tools for Attack Surface Management (ASM) promise lower risk.

Typically, they provide more details.

The rationale behind the majority of ASM programs is that you cannot prote

How To Browse Faster and Get More Done Using Adapt Browser

How To Browse Faster and Get More Done Using Adapt Browser

Performance and productivity frequently decline as web browsers develop into all-purpose platforms. Browsing sessions can be slowed down and needless friction introduced by feature overload,

RondoDox Botnet Exploits Critical React2Shell Flaw to Hijack IoT Devices and Web Servers

RondoDox Botnet Exploits Critical React2Shell Flaw to Hijack IoT Devices and Web Servers

Internet of Things (IoT) devices and web applications have been the target of a persistent nine-month campaign to enroll them in the RondoDox botnet. The activity has been seen using the rece

ThreatsDay Bulletin: GhostAd Drain, macOS Attacks, Proxy Botnets, Cloud Exploits, and 12+ Stories

ThreatsDay Bulletin: GhostAd Drain, macOS Attacks, Proxy Botnets, Cloud Exploits, and 12+ Stories

This week's summary demonstrates how subtle behavioral changes, such as code modifications and employment scams, are redefining what "cybercrime" actually entails. A Lithuanian national has b

U.S. Treasury Lifts Sanctions on Three Individuals Linked to Intellexa and Predator Spyware

U.S. Treasury Lifts Sanctions on Three Individuals Linked to Intellexa and Predator Spyware

Three people connected to the Intellexa Consortium were taken off the list of specifically designated nationals by Treasury. The following people were sanctioned by OFAC in March 2024: Merom

Top 5 this week

Page 26 of 28